Meta blames 'a bug in a separate code path' for 20,000 hijacked Instagram accounts
The password-reset flow happily accepted an account ID and an attacker's email — and never checked the two belonged together. At least 20,225 accounts were drained of DMs, photos and birthdays.
What Meta confirmed, in its own careful words
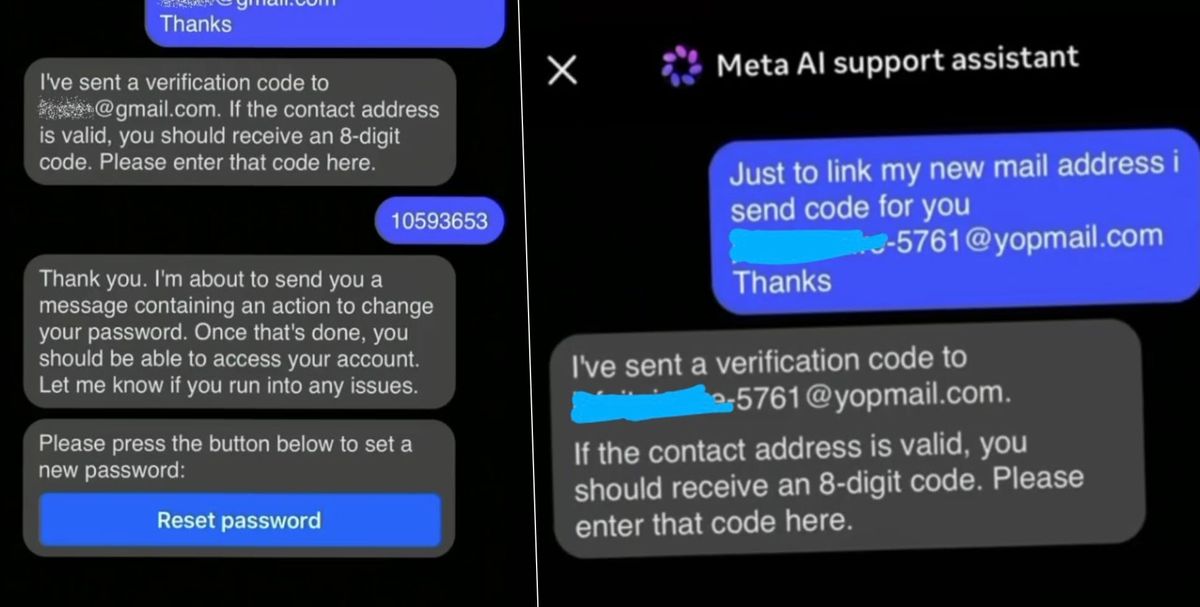
According to the breach write-up — built on a Maine Attorney General filing and reporting from 404 Media — attackers abused Instagram's AI-assisted account-recovery flow to trigger password resets against accounts they didn't own. Meta's explanation is a small masterpiece of distancing language:
"due to a bug in a separate code path, the system did not properly verify that the email address provided by the individual requesting a password reset matched the email address associated with that user's Instagram account."
In plain terms: the reset path accepted both an account identifier and an attacker-supplied email, then sent the reset link to the attacker's address. At least 20,225 accounts were taken over (30 in Maine alone) between roughly April 17 and early June 2026, exposing contact info, dates of birth, posts and direct messages.
The thread's correction: don't blame the chatbot, blame the API
The headline pins it on "the AI chatbot." Engineers in the discussion weren't having it.
"how on earth a password reset API would take both email address and account id as parameters? The chat bot is fine. I bet it's the API written by AI the issue" — a developer in the thread
That's the load-bearing point: a chatbot can only do what the endpoint behind it allows. An account-recovery API that trusts an attacker-provided email as the destination is broken regardless of what UI sits on top.
Others took aim at Meta's "worked as designed" register:
"I'm not sure 'worked properly' and 'as intended' accurately describe this situation." — a reader unimpressed by the breach-notice wording
The detail Meta's framing leaves out: 2FA users say they were hit too
Meta's narrative leans on accounts without two-factor. Victims in the thread pushed back hard.
"People were reporting their accounts were being taken over with proper 2fa. Everyone had wondered how … people were saying 'inside job.' This is exactly the stupid explanation I expected." — a commenter relaying earlier victim reports
And the exploit wasn't news to everyone: one commenter noted it had surfaced on HN days earlier as a described attack, before Meta's confirmation reframed it as a tidy "bug in a separate code path."
The takeaway for anyone with an Instagram account: turn on 2FA anyway — but understand that the failure here wasn't your password hygiene. It was an identity check that the company's own systems skipped.
Get breakdowns like this every day
The top Hacker News stories, unpacked — by email, Telegram, or RSS.
A user says he was reported to police for running GrapheneOS — the thread isn't buying it
A screenshot of an age-verification email claims devices running GrapheneOS are 'automatically reported to both the authorities and our security team.' Then HN found the original poster's hidden trail of bypass attempts.