His real ID unlocked stream keys for every World Cup camera
The Angular app showed an access-denied page. The backend handed over everything: RTMP ingest URLs and stream keys for all five camera angles of every World Cup 2026 match. He confirmed a live feed in VLC.
The flaw was textbook: roles were checked client-side only. The server never validated the JWT, so the APIs served live broadcast infrastructure to anyone who registered on FIFA's public Agent Platform. Push to the RTMP endpoint and you replace the feed on TV worldwide.
The twist: FIFA never responded. No acknowledgment, no thank-you, no bounty — they just silently patched it. Half the thread asked why he reported it at all.
"Client says access denied. Server says here's everything."
The researcher registered on FIFA's public Agent Platform with his real ID, got added to their Microsoft Entra tenant, and found the whole thing hinged on one mistake: the Angular front-end checked the JWT for a no-roles marker and rendered an access-denied page, while the backend APIs checked nothing at all.
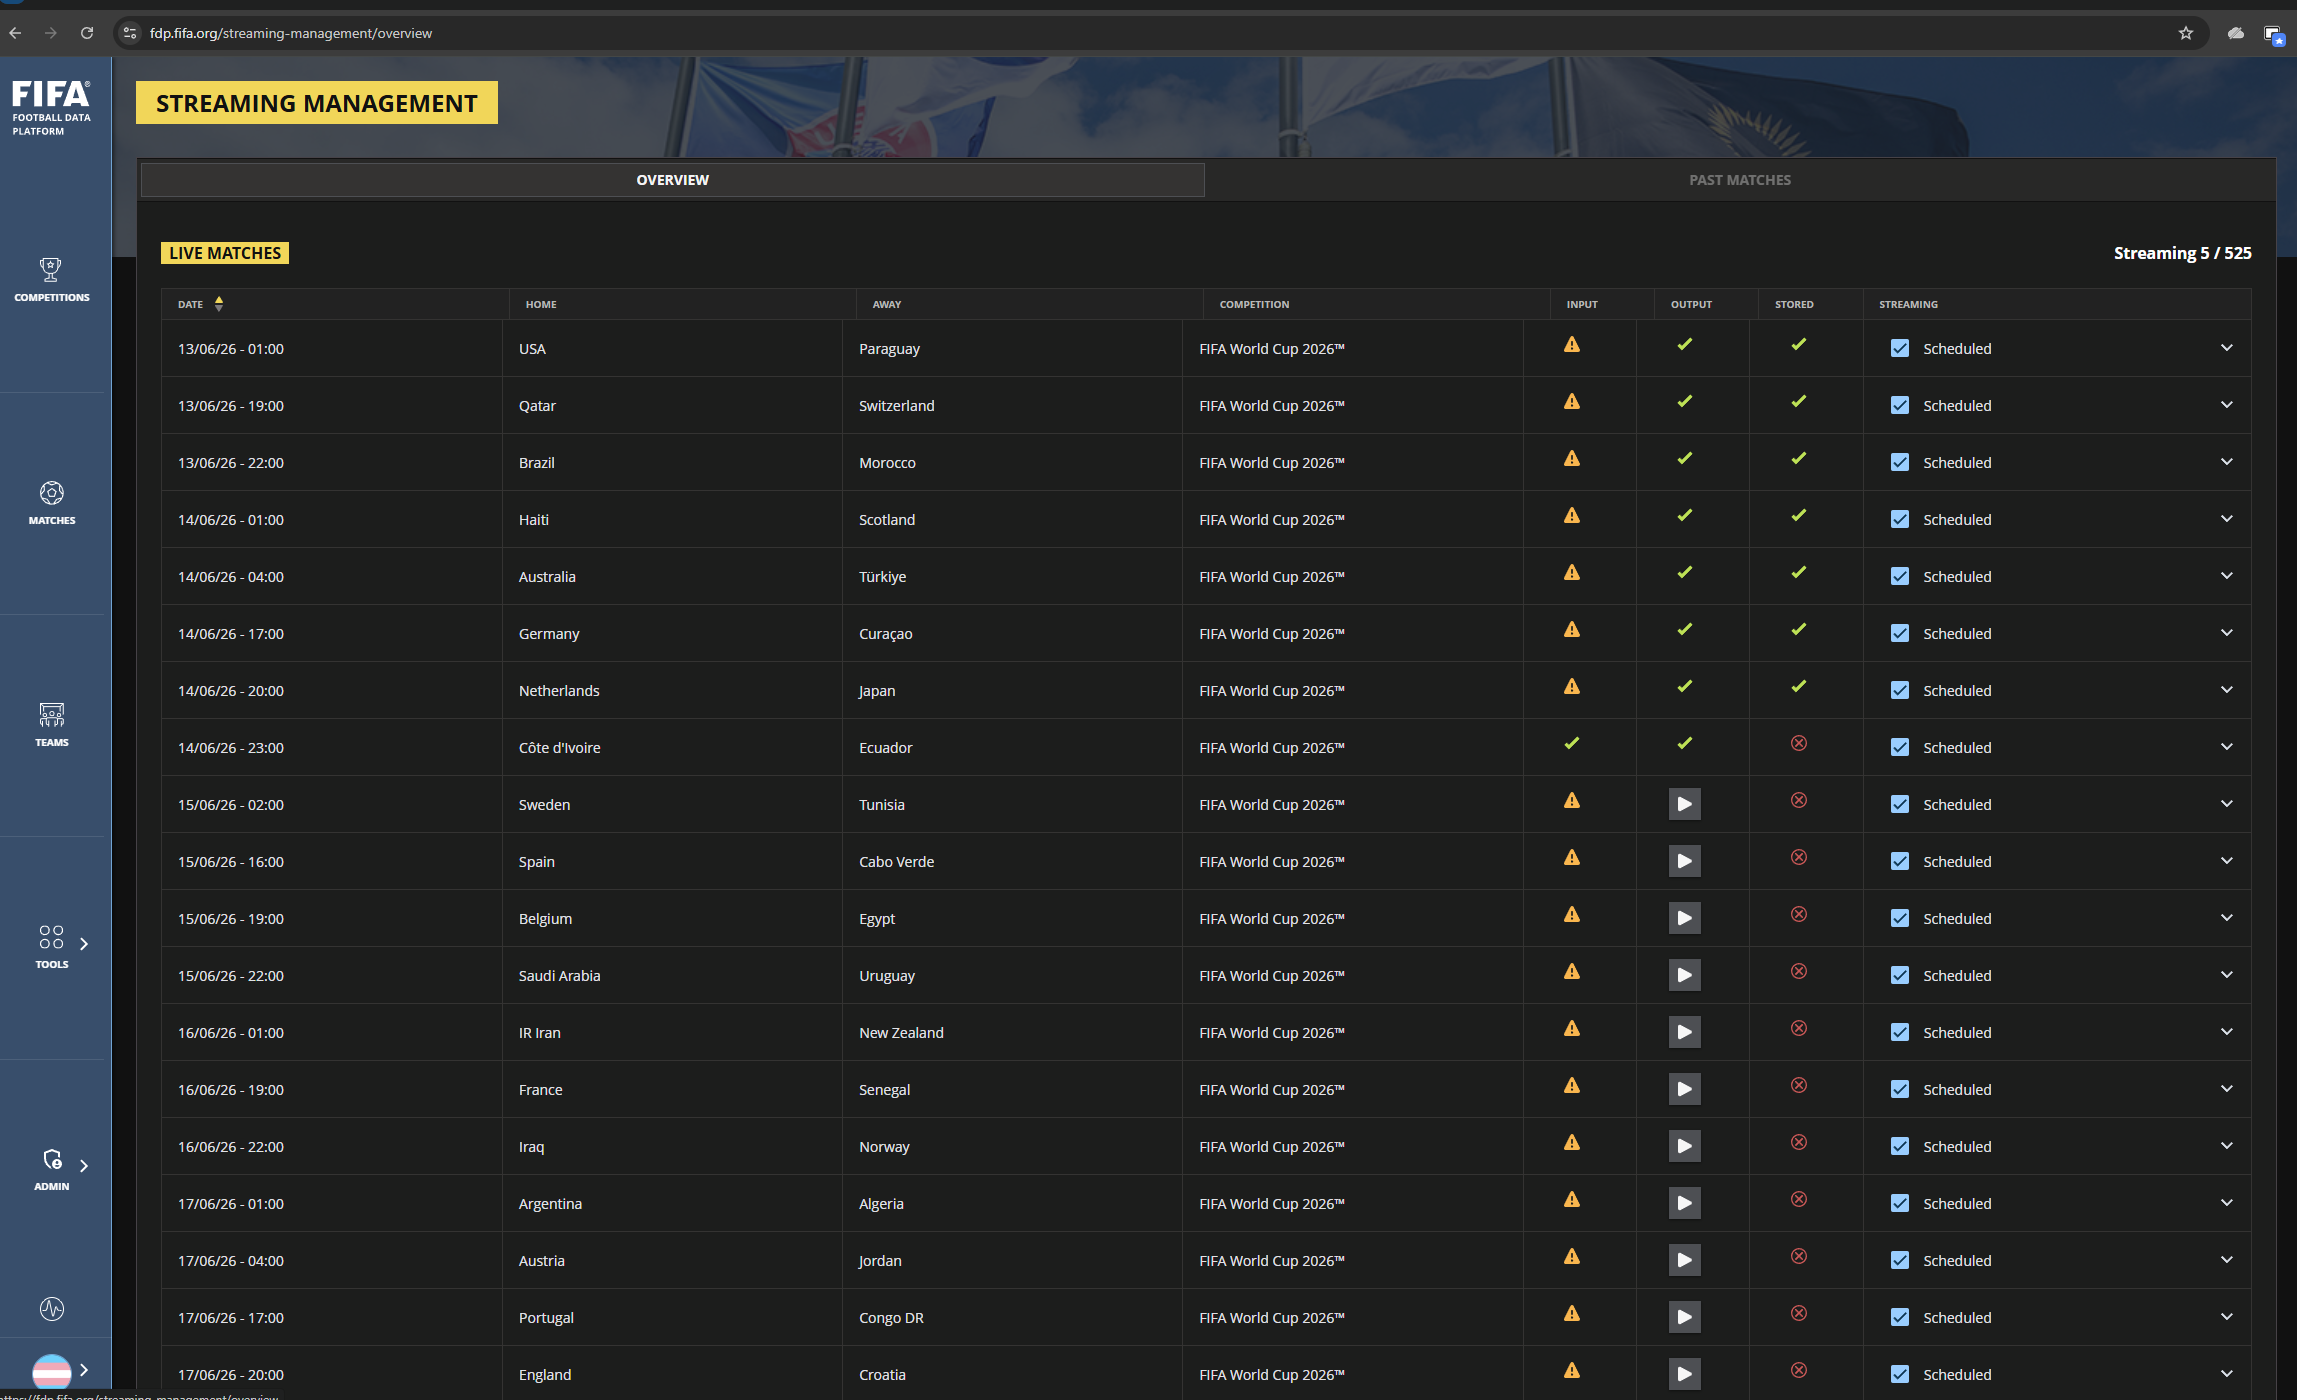
What the backend actually served
Behind the denial screen, the Streaming Management panel exposed live World Cup 2026 broadcast infrastructure: RTMP ingest URLs and stream keys for every camera feed across all five angles, plus write access to match stats, commentator notes, and the live score system. The streaming panel laid it all out.
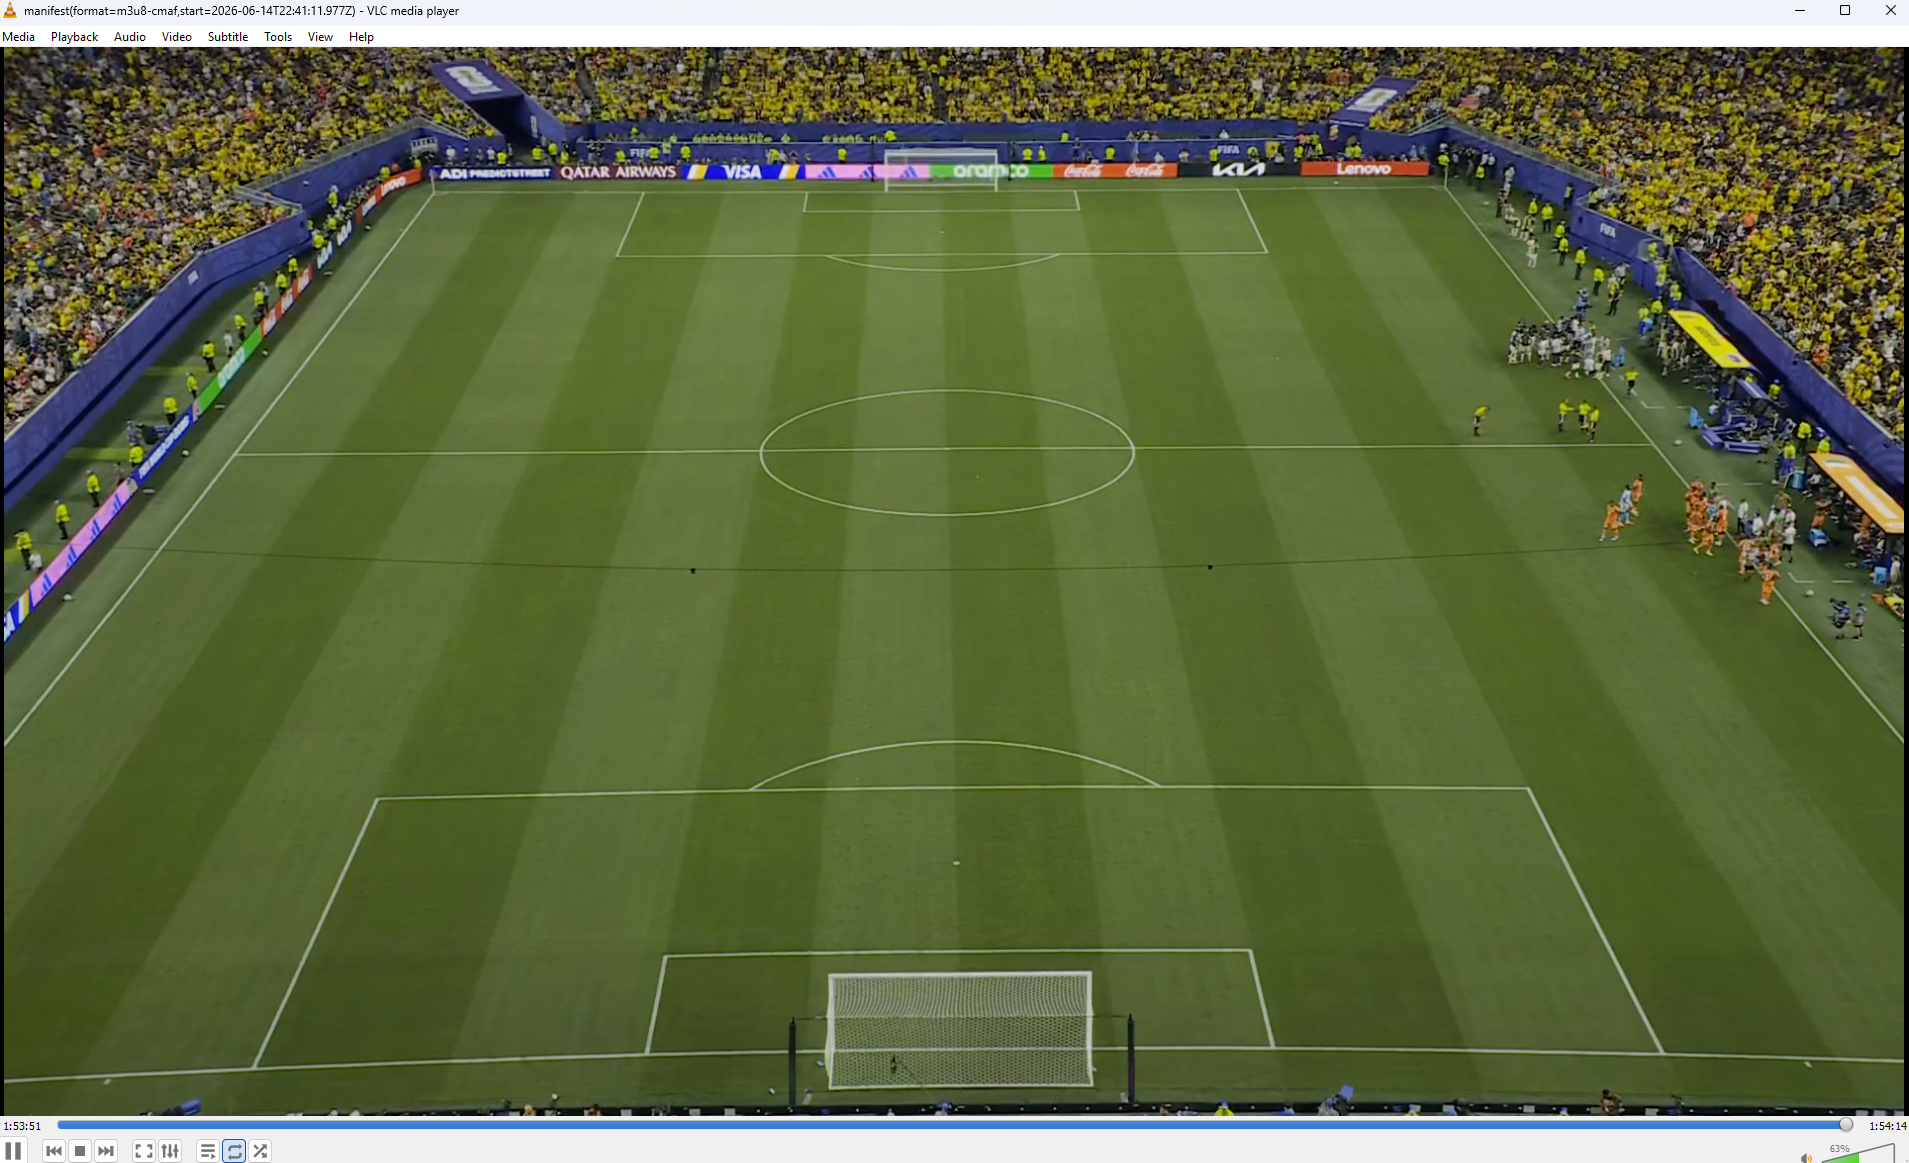
Then he confirmed a real camera feed playing live in VLC. Not a mockup: an actual stadium camera.
Those ingest URLs are the literal pipe from stadium cameras into FIFA's broadcast distribution chain. Push arbitrary video to the endpoint with the exposed stream key and, in the worst case, every TV network receiving the feed shows whatever you sent.
A précédent from Qatar 2022
The thread surfaced that this is not FIFA's first rodeo. A former GitHub and GitLab cofounder had done the same dance for the last World Cup.
I did something similar for Qatar 2022 and got access to roster submission … their promised "token of appreciation" never came. (Although … they didn't sue me, so I guess that's a win.) — Zach Holman, cofounder of workon.co, formerly GitHub and GitLab
A broadcast-industry engineer added the load-bearing skeptic's note: it's not certain these feeds reach broadcasters at all.
Do you know these feeds actually go to broadcasters? They could be internal feeds for refs, match review … The broadcast contribution feeds I've seen … are MPEG-TS, not via RTMP. — a software developer focused on the media industry
The reporting paradox
FIFA fixed it and said nothing — no acknowledgment, no thank-you, no compensation, despite the researcher escalating to CISA and the FBI. That silence flipped part of the thread against the disclosure itself.
This is honestly one of the only instances where I am like "you're an idiot for reporting this" … Paired with how shitty of an org FIFA is, I personally would have just leaked this. — a commenter weighing the reach against FIFA's track record
The uncomfortable rule underneath: when an organization offers nothing for a good-faith report — not even a reply — it teaches the next finder to either stay quiet or sell. A client-side-only auth check is the textbook bug. The harder failure here is an incentive system that punishes the person who chose Rickroll over ransom.
Get breakdowns like this every day
The top Hacker News stories, unpacked — by email, Telegram, or RSS.
Bash can open a TCP socket and fake an HTTP request without curl
An engineer needed to ping a health endpoint between Docker containers. The image had no curl, no wget, no nc. So he opened /dev/tcp/service/8642 and typed the HTTP request by hand.