One researcher found 333 Tor exit relays quietly intercepting SSH sessions (kaba.cx)
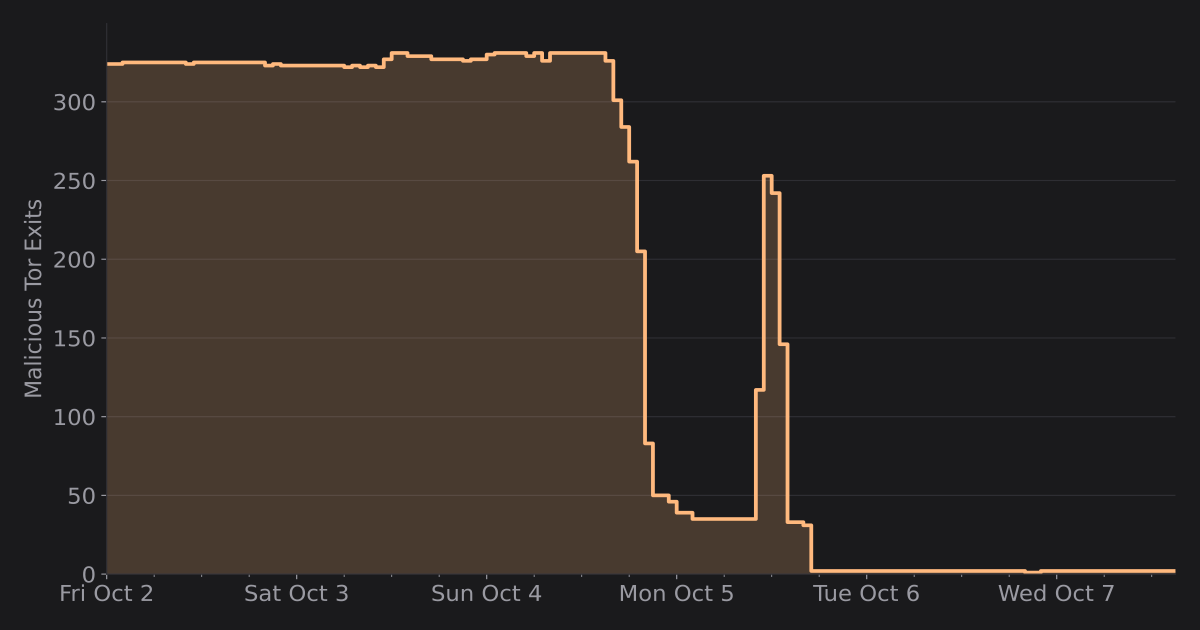
A scan that pinned each of ~3,000 exits and compared SSH fingerprints exposed 333 compromised relays. Interception began 2 October; BadExit flags followed on the 4th.
The thread's sharper point: key-based login would have denied the interceptors the passwords, and the fingerprint warning only reaches users who keep a known-hosts file.
Sign in to save