The first Switch 2 jailbreak starts inside SmileBASIC, a Switch 1 game
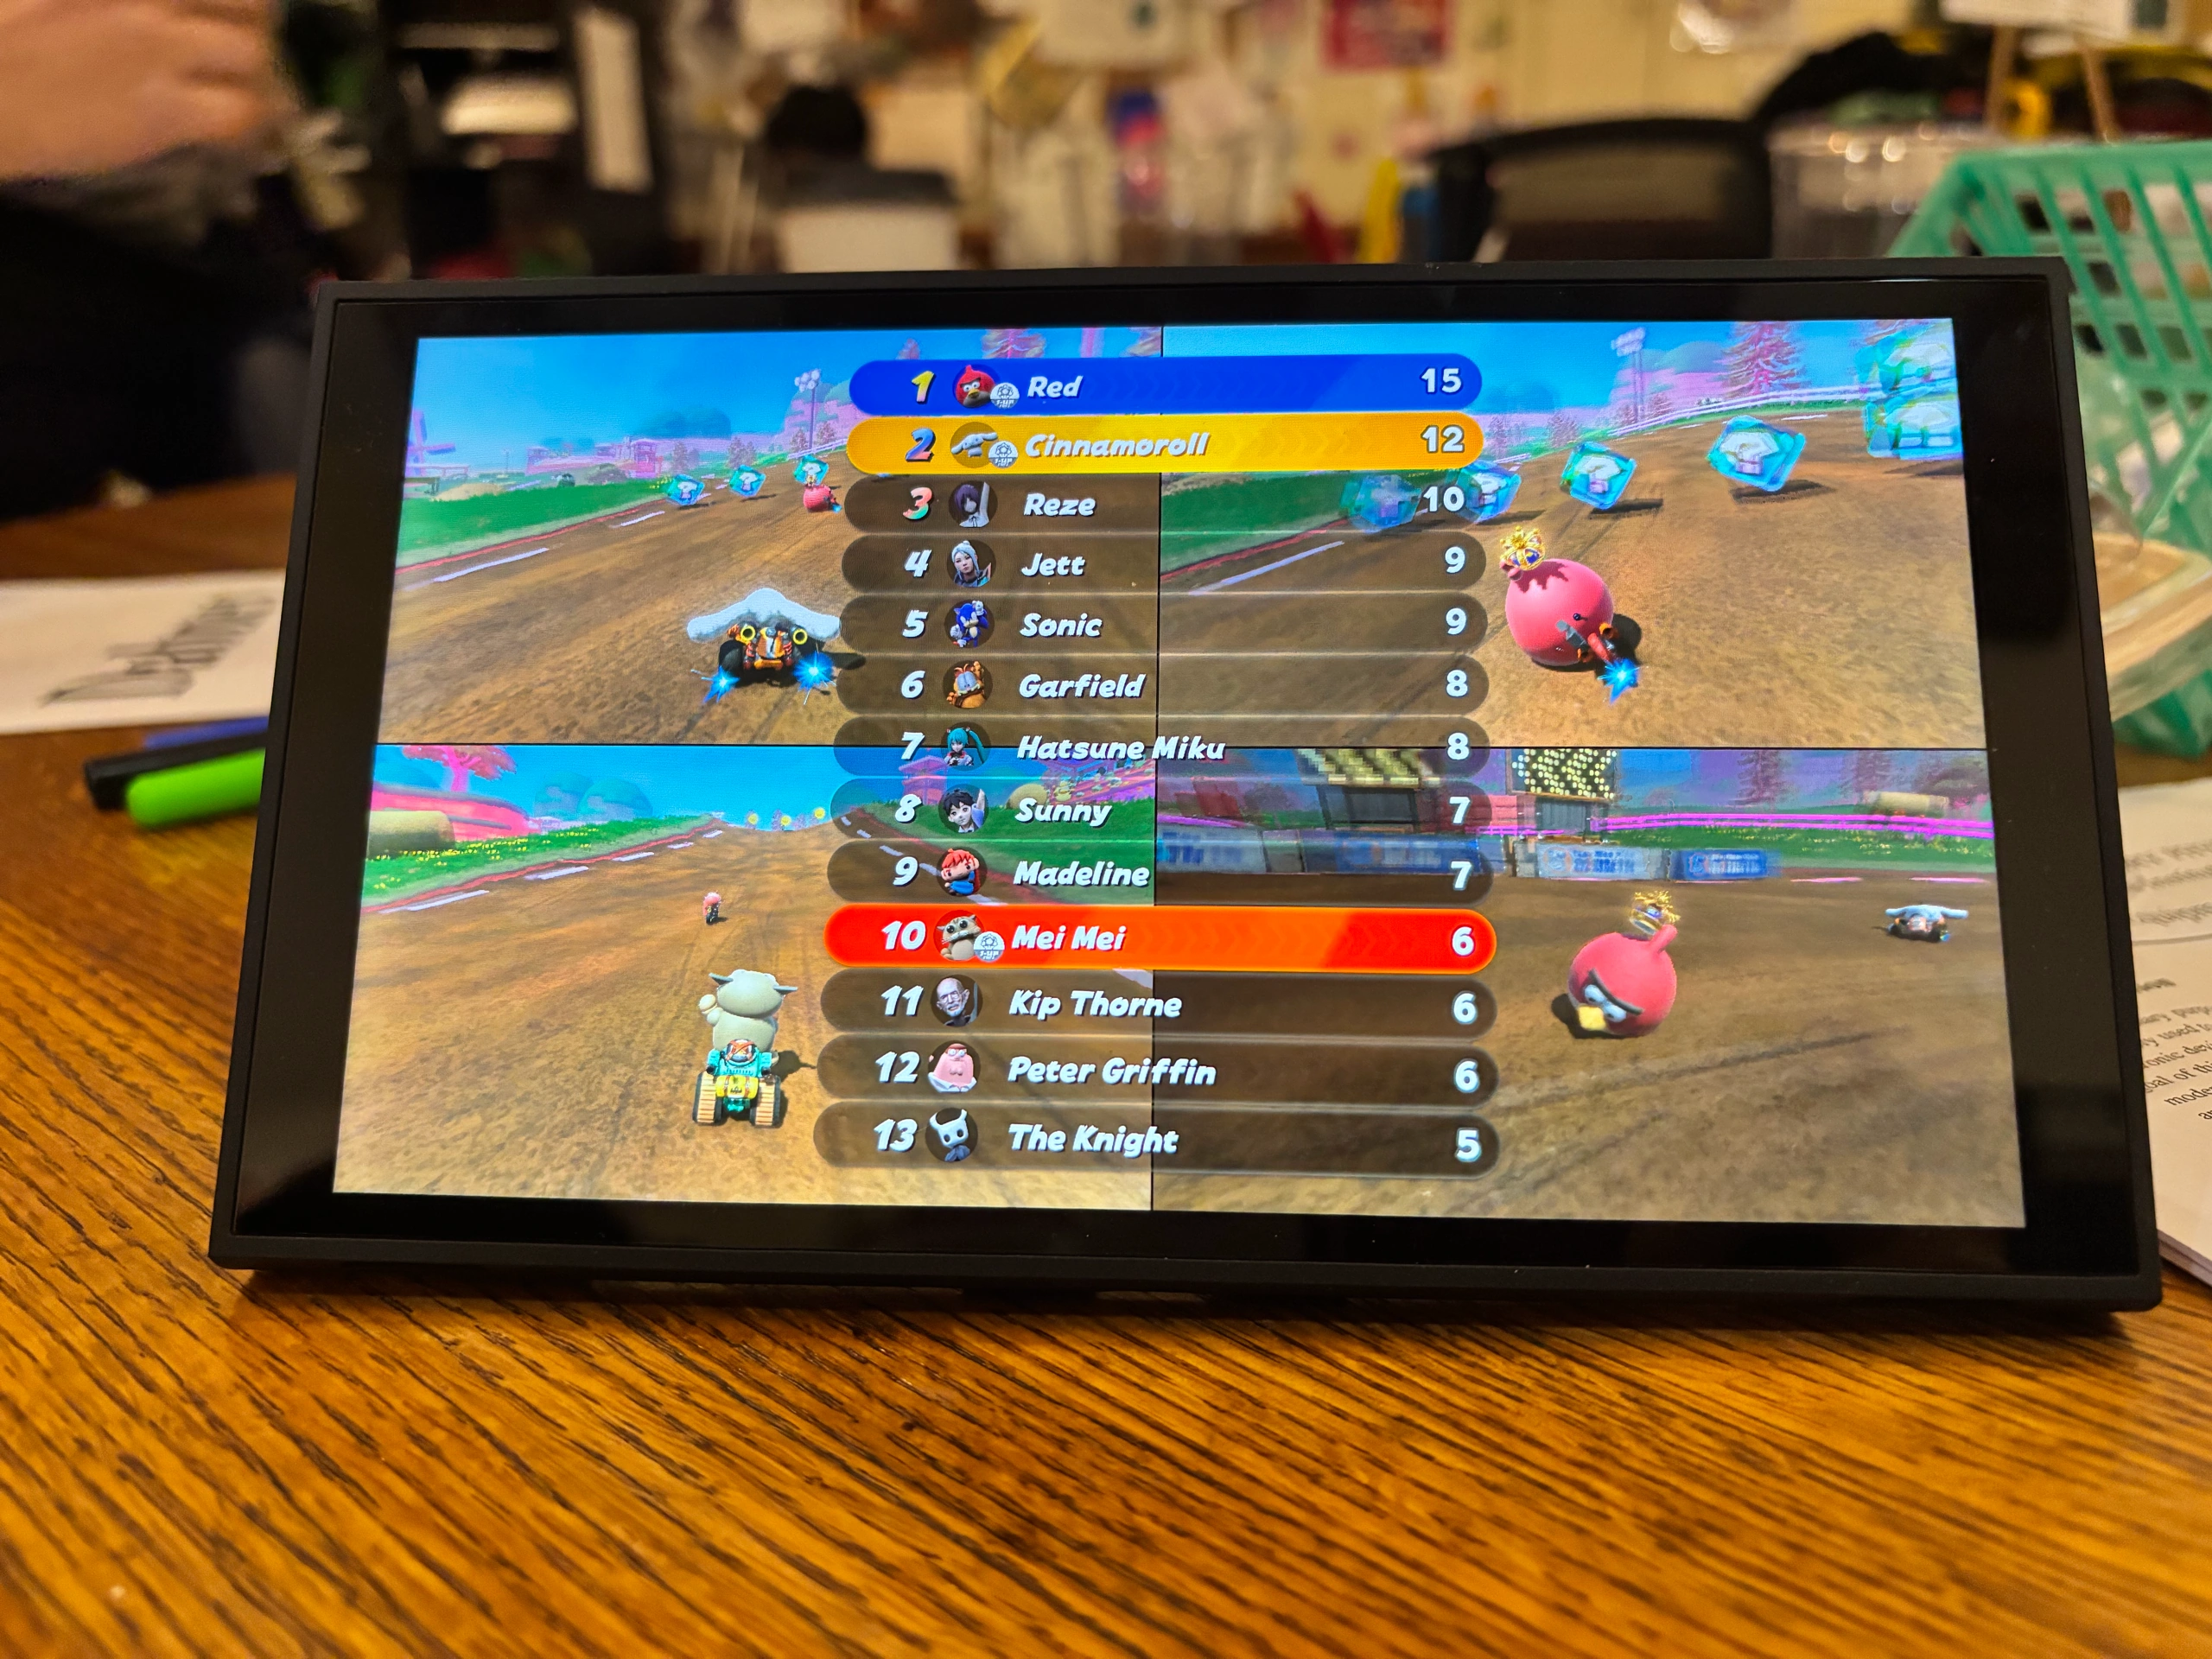
The author wired two consoles to two JetKVMs and a Bluetooth switch-flicker so AI agents could press power after every crash. The first demo was a Mario Kart World mod, "entirely vibecoded in a day".
A 32-bit integer overflow in SmileBASIC's array REMOVE handling gives memory read and write on the Switch 1, where there is no pointer authentication. A path-normalization overflow then reaches the filesystem service.
The exploit is tethered, runs on firmware 23.0.1, and took about two weeks of real work.
Why a BASIC game on the old console
The write-up dated 18 October 2026 describes ns2jb, a software-only, tethered jailbreak for Switch 2 firmware 23.0.1. It gives arbitrary native code as any ordinary sysmodule and as the built-in fs sysmodule. The author's first idea, a WebKit n-day through a captive portal, failed against execute-only memory, pointer authentication and control-flow integrity.
The way in was a Switch 1 game, because Switch 1 code lacks pointer authentication and its root of trust is already owned. A 32-bit integer overflow in how SmileBASIC removes elements from an array lets an out-of-bounds copy corrupt the array so its elements are treated as strings, giving arbitrary reads and writes and eventually ROP on the Switch 2.
From a path buffer to code in any sysmodule
A buffer overflow in path normalization, a 0x301-byte temporary heap buffer, corrupts a neighboring cache entry in the filesystem service. Setting SmileBASIC's saved process ID to 1 then grants full filesystem permission. The loader verifies two signatures, but because fs serves the content, swapping the executable's filesystem handle after the header hash was submitted lets custom code load while both checks pass.
The harness mattered as much as the bugs: two consoles, two JetKVMs for controller input and HDMI video, and a Bluetooth switch-flicker let coding agents recover from crashes unattended.
What the thread worried about
The loudest fear was game dumps and recompilations. One commenter said that with decrypted fs read/write, console exclusives could soon run on arbitrary hardware, and called the camera-and-KVM approach "a very strong paradigm for this sort of hardware work".
A builder who ports games to DOS and Classic Mac with Claude described the same rig on a smaller scale:
"For a while I was doing the SDcard swap thing" — a hobbyist who has Claude drive real vintage hardware
He replaced it with a USB input device for hands, a capture dongle for eyes, and a smart plug for power cycling. Not everyone expects Nintendo to suffer.
"Given the continuing success of the Switch 1 even after such emulators existed, I doubt this will pose a serious problem for Nintendo." — a commenter pointing to years of Switch 1 emulation
The post itself is silent on whether Nintendo can patch the entry point, and the author lists other built-in sysmodules as unexplored.
Get breakdowns like this every day
The top Hacker News stories, unpacked — by email, Telegram, or RSS.
A 360M-parameter model pretends to be a terminal, and vim and tmux still work
WorldTUI has no shell or filesystem behind it. Each keypress goes in, and the model predicts which screen rows change and where the cursor lands.