Five cross-tenant Azure bugs, one shared API Management instance, $200,000 in bounties
Azure Logic Apps brokers connections through a shared gateway, so one validation mistake let a tenant act as another.
A Binary Security researcher found that Azure API Connections swap a user's token for the backend's through one shared API Management instance, so security rests on input validation. Path traversal in DynamicInvoke read a secret from another tenant's Key Vault; later bypasses reopened the hole after each fix.
One shared gateway, five ways across the tenant boundary
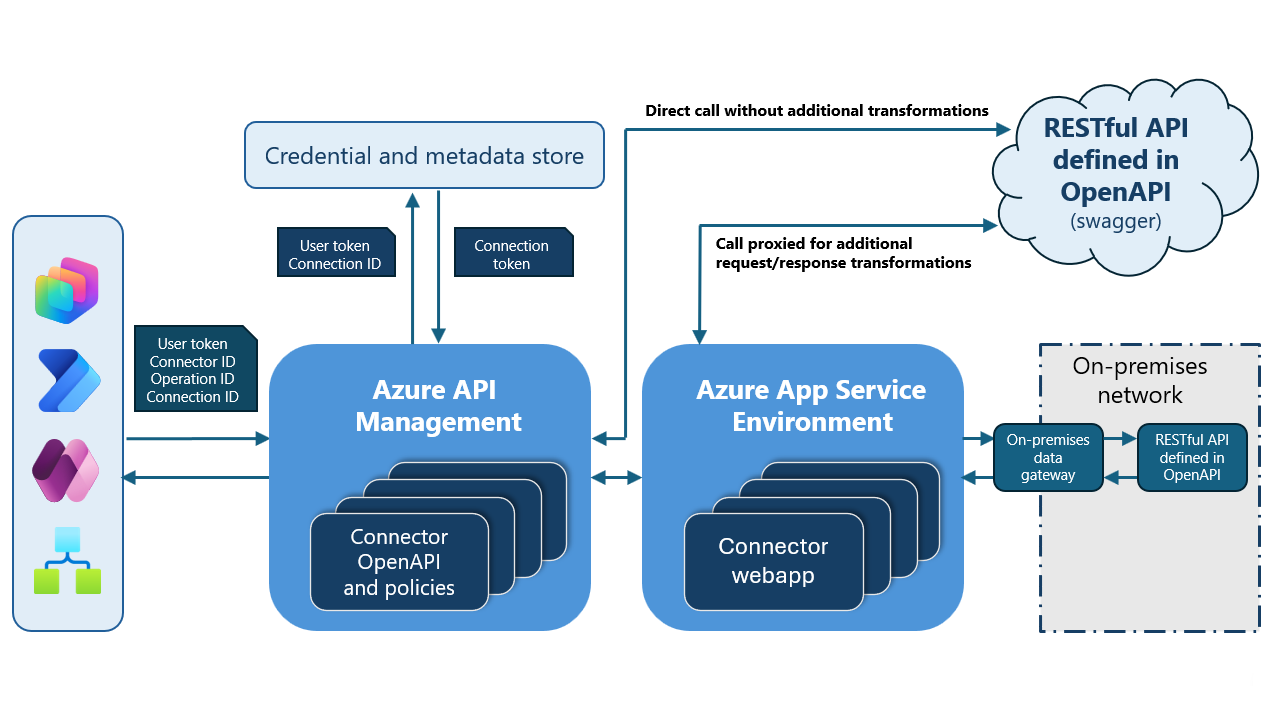
Binary Security's write-up, presented at Blue Hat Asia 2026, covers five critical elevation-of-privilege issues in Azure API Connections, part of Azure Logic Apps, that together earned researcher Haakon Wik Gulbrandsrud $200,000. Connections are brokered by a shared Azure API Management (APIM) instance that swaps a user's connection token for the backend's configured token. ARM's DynamicInvoke and proxy endpoints reach APIM directly, and that request can act on any connection, so the boundary is only as good as input validation.
The compromises: path traversal through DynamicInvoke read a secret from another tenant's Key Vault. After a path restriction, undocumented siblings such as DynamicList allowed the same traversal, enabling a cross-tenant SQL write. Consumption Logic Apps implicitly use Version 1 connections, and a hidden host.api.RuntimeUrl parameter redirected calls to a victim's connection. An exact-match fix was bypassed by traversal because validation ran before path normalization, and a later fix left the original path unvalidated.
Fixed, then broken again
One commenter summarized the sequence with some heat:
"Vulnerability was reported. They fixed it - incorrectly. Reported again. They fixed it this time... and broke the previous fix. So it's vulnerable again."
The researcher's own verdict is milder: he calls the fix timelines reasonable and says he was overall satisfied, with some disagreements with MSRC. Another reader found the sharper incentive point:
"Reporting cross-Tenant issues as an outsider with a vulnerability chain gets you $$$. Reporting "theoretical" issues with validation as an Employee gets you a lot of questions as to why you were looking."
For Logic Apps users the lasting fact is the design: Microsoft closed the dynamic endpoints entirely instead of validating them, which suggests the shared-gateway model cannot be patched into safety one path at a time.
Get breakdowns like this every day
The top Hacker News stories, unpacked — by email, Telegram, or RSS.
Tangled relaunches as a federated Git forge where issues and pull requests live in the repository
Issues, pull requests and comments are now chains of Git objects inside the repo, so discussion moves with the code.