AMD's updater downloaded code over plain HTTP and ran it. The bug bounty called it out of scope (mrbruh.com)
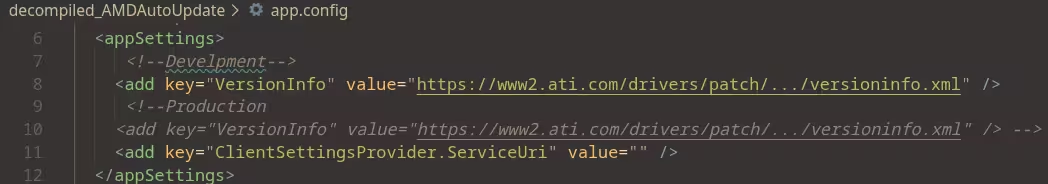
Disclosure ran 124 days, when the fix was essentially adding an 's' to a couple of URLs. The eventual "signature verification"? A CRC32 checksum — which any attacker can trivially recompute.
Known security voices reframed it: AMD never denied it was a vulnerability, only that it was in scope — and at big vendors, bounty teams are measured on payouts. The dark comedy: the updater may be too broken to exploit.
Sign in to save