An Edge exploit chain with no memory corruption starts by visiting microsoft.com (blog.orange.tw)
Edge auto-creates and signs into a Microsoft account profile when you visit a Microsoft site, and a CORS misconfiguration on assets.msn.com lets any website read the signed-in email. From there the chain abuses a navigation throttle, a popup whitelist and a diagnostic-log file write to launch a planted telnet.exe.
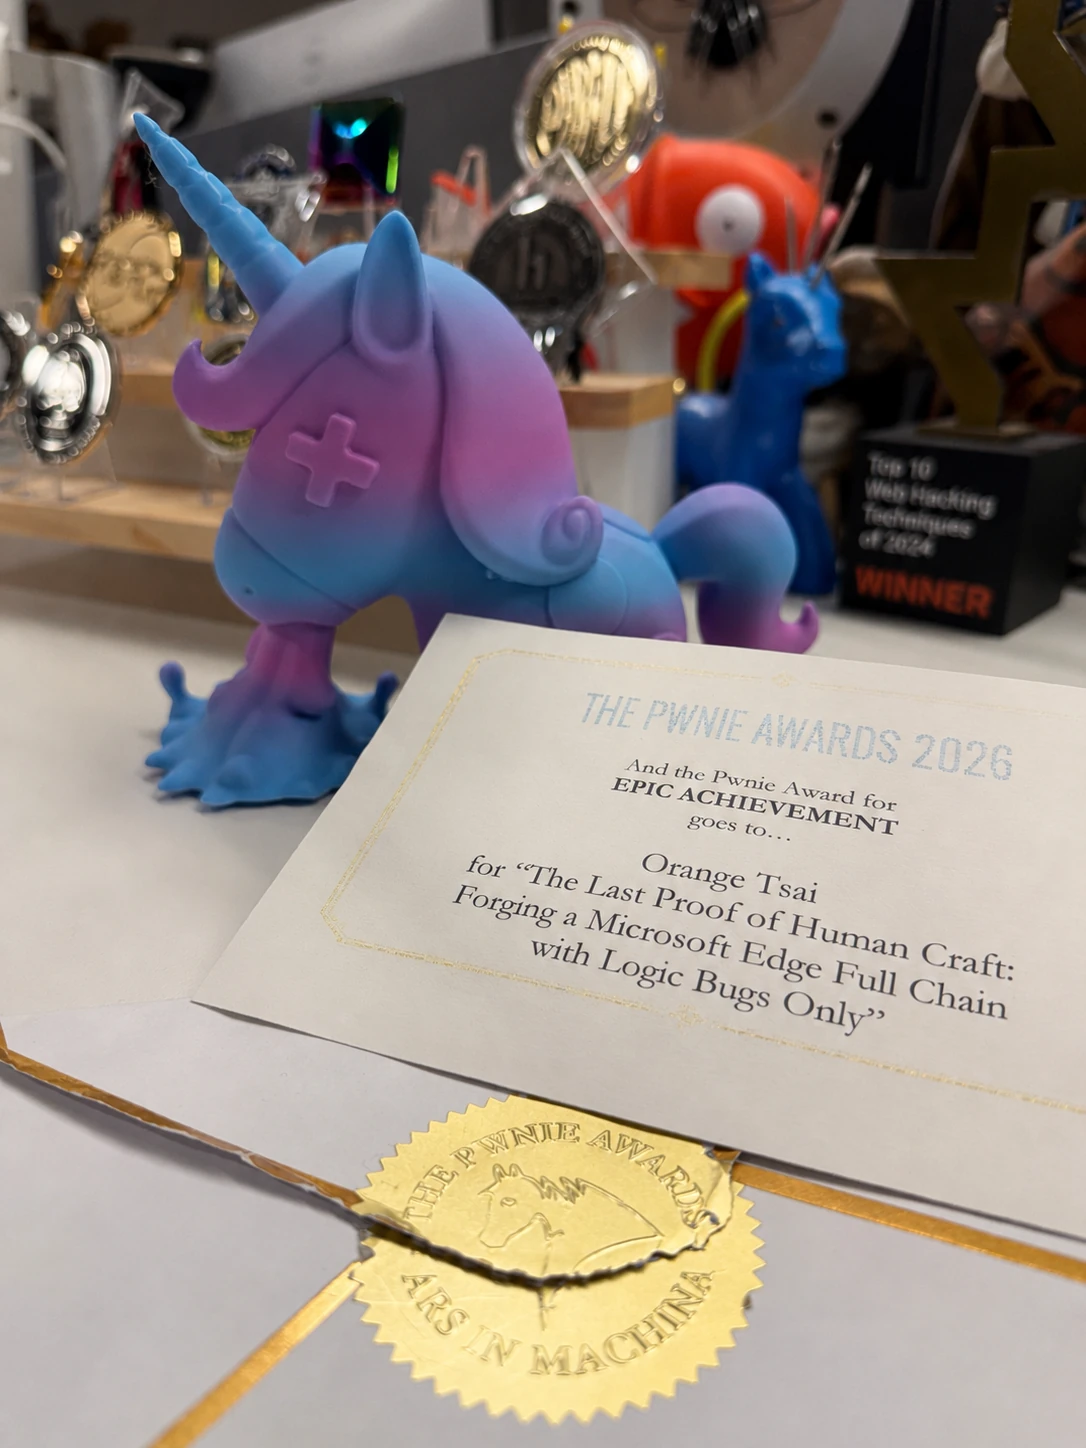
It earned $175,000 at Pwn2Own Berlin 2026, and its author says no AI was used to build it.
Sign in to save