Topic

Web & Browsers

60 stories

Discord will publish public-channel messages to search engines from mid-December (discord.com)

Admins can pick which channels participate or switch them all off, in Server Settings under Web Presence, and members get a single toggle in User Settings under Data and Privacy. Public channels are on by default, except member settings default to off in the EU, UK, Canada, Brazil, Australia and South Korea.

The thread worried less about Google than about who can be linked back.

🌍Other ★ 254 · 💬 134 · 10h ago · #privacy#social media#web#Discord

Not just a headline — the discussion unpacked

The top HN threads: facts from the discussions, both sides, insider voices. Email, Telegram, or RSS.

A crawler pulled 145.5 GB from 3D-model sites in 34 hours, including 54.8 GB of adult content (open3dlab.com)

Between October 15 and 16, one AWS address made 26,429 requests across nearly all 18,926 projects on Open3DLab, SFMLab and SmutBase, then downloaded 1,027 files from 712 of them. Roblox never answered two emails, and the site's claim that this was AI training data is its own inference.

Hacker News argued about the site's own licensing, then about how to block the next crawler.

A Brotli bug found in February shipped no fix until now, and it reaches far beyond Node.js (aikido.dev)

CVE-2026-111497 (CVSS 9.2) lets a crafted Brotli stream trigger an out-of-bounds write, and it works in both directions: a malicious server can hit a client, and a malicious client can hit a server.

The thread argued about the name. Whether HTTP is really exposed turned out to depend on one setting.

🚀Tech ★ 281 · 💬 140 · 3 days ago · #open source#security#web#Aikido#Brotli#curl+2

UUIDv7 only promises uniqueness, and Python's version can run ahead of your clock (alexsci.com)

Alex Scott's post argues the three properties people credit to UUIDv7, monotonic order, a trustworthy creation time and unguessability, are not guaranteed by RFC 9562. Even Postgres warns that an extracted timestamp may differ from the creation time.

Commenters said that misses the real reason to use it: keeping new rows together in the index.

🚀Tech ★ 114 · 💬 99 · 4 days ago · #data#programming#web#Postgres#Python#RFC 9562+1

eMudhra quits the global TLS certificate business after its weak CA keys were revoked (emudhra.com)

eMudhra will withdraw from issuing public TLS certificates, keeping revocation services running until every issued certificate has expired or been replaced. Customers get replacements free through partners.

In the thread, a commenter reports that an up-to-date iPhone was still trusting the compromised CAs nearly five days after the report.

📈Biz ★ 940 · 💬 634 · 5 days ago · #big tech#security#web#Apple#eMudhra#Google Chrome+1

Quad9 will leave France rather than block piracy domains for a Qatari broadcaster (quad9.net)

beIN says the domains infringe its sports broadcast rights. Quad9 says it has no user database and cannot tell who is in France, and that about 20 other French cases covering hundreds of domains are pending.

Its CTO appears in the thread to explain why leaving beats complying.

🌍Other ★ 1.0K · 💬 365 · 5 days ago · #policy#privacy#web#ARCOM#beIN#Quad9

Arc browser stops working on December 22, and The Browser Company cites security (arc.net)

The Browser Company says keeping a browser secure is growing work with AI, so its engineers move to Dia. On mobile, AI features and tab sync end on November 23.

Dia imports Arc passwords, bookmarks, extensions, history and tabs; Spaces become Profiles and Folders become Tab Groups.

📈Biz ★ 230 · 💬 210 · 5 days ago · #startups#web#Arc#Dia#The Browser Company

PHP patched two unauthenticated RCE bugs after the CVE IDs leaked two days early (thephp.foundation)

PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 shipped on 21 October, a day ahead of plan, after the CVE IDs leaked. Both bugs score CVSS 9.2 and need no login, and a proof-of-concept video went up by mistake.

In the thread, an admin racing across several servers said a three-line nginx rule blocking multipart uploads had been quietly protecting a machine he could not shut down.

🚀Tech ★ 683 · 💬 336 · 6 days ago · #open source#security#web#Calif#Chainguard#PHP+1

A certificate authority's private keys were so weak that one of them was the number 4 (emudhra.we-have-a-problem.com)

Eight eMudhra intermediate CA certificates, valid since April 2025, had keys that could be computed from the certificates themselves. A commenter pulled out the scalars: 4, 56, 66, 115, 155, 156, 230, 237.

Firefox shipped a fix in hours via OneCRL; a Mozilla engineer in the thread says everything outside the big browsers is still exposed.

🚀Tech ★ 659 · 💬 340 · 7 days ago · #security#web#eMudhra#Firefox#Mozilla+1

A $50 network of 50,000 fake statistics pages is now cited by ChatGPT and a Qatari bank (peec.ai)

Metehan Yesilyurt of Peec AI built about 50,000 pages of invented stats plus 15,000 listicles with GPT-4.1. Google demoted the site after two updates, but ChatGPT kept crawling it, logging over 600,000 bot requests in 30 days.

The fake figures reached an academic paper and investment research from Qatar's largest financial group.

🚀Tech ★ 323 · 💬 188 · 7 days ago · #AI#web#ChatGPT#GPT-4.1#Peec AI+1

Let's Encrypt moves to six remote validation perspectives ahead of a December deadline (community.letsencrypt.org)

Let's Encrypt is adding two remote perspectives, raising the total from four to six, to meet CA/Browser Forum rules that take effect December 15, 2026 and call for at least five. The point is to make BGP hijacks of domain validation harder.

Staging starts October 27 and production rollout is planned for November 10.

DeepSeek now sells web search and page fetch for $0.75 per 1,000 requests (api-docs.deepseek.com)

DeepSeek published Search and Fetch APIs at $0.75 per 1,000 successful requests, billed only on HTTP 200 responses. Calls routed through Claude Code, Codex or DeepSeek's own harness are free until 00:00 Beijing time on November 1, 2026.

The first reply was a price check: Kagi's API runs $12 per 1,000 searches. Then a hobbyist who built his own agent tools said the big labs' bundled search costs 15-20x more than his.

🚀Tech ★ 551 · 💬 260 · Oct 19 · #AI#dev tools#web#Brave Search#Claude Code#Codex+2

Jake Archibald benchmarked JPEG XL against AVIF, and AVIF won most of the web (jakearchibald.com)

Archibald tested avifenc, libjxl, jixel and cwebp on an M4 Pro, scoring with SSIMULACRA2. JPEG XL lost on lossy photos and screenshots (30-90% larger), but dominated lossless and can recompress existing JPEGs 9-20% smaller.

Commenters disputed whether the benchmark or Chrome's earlier decision was the real story.

🚀Tech ★ 204 · 💬 144 · Oct 17 · #dev tools#web#AVIF#Chrome#Jake Archibald+1

A joke domain became a small front in geopolitical warfare (sprocketfox.io)

The account traces how an apparently disposable internet asset acquired strategic meaning once people relied on the surrounding service for public flight and sensor data.

It is a reminder that infrastructure dependencies can hide in names, hosts, and volunteer projects long before anyone writes a procurement plan.

🚀Tech ★ 764 · 💬 117 · Aug 20 · #policy#security#web#SondeHub

Cloudflare analytics injection exposes the proxy trust boundary (news.ycombinator.com)

Several users confirmed that Web Analytics can add JavaScript when Cloudflare is proxying traffic, while DNS-only domains do not pass through that HTML-rewriting path.

The sharper complaint was the control surface: one commenter said they had to enable analytics merely to find the setting that disables it.

GitHub’s rough day revives the Azure migration question (news.ycombinator.com)

Users reported failures across Microsoft services and pointed to GitHub’s long-running move toward Azure; neither observation alone established the root cause.

A second explanation was load: commenters cited rapid growth in commits and new accounts as AI-assisted development turns GitHub into a much busier system.

Cloudflare's AI push revives a platform trade-off (opensauce.it)

Cloudflare's Workers, Durable Objects, and R2 gave readers practical reasons to defend the platform. Critics focused on who gets excluded when a central layer decides what a legitimate client looks like.

The dispute was not about whether the company ships. It was whether the convenience of an opinionated platform leaves room for nonstandard clients on the open web.

Unicode's ghost characters reveal how a standard preserves mistakes (dampfkraft.com)

The essay follows characters that entered reference works through transcription errors and historical ambiguity. Once encoded, they become part of the compatibility burden that keeps old text readable.

HN readers described the conservative trade-off: extra invalid characters are often safer than deleting a character that later proves to be real.

uBlock Origin gives Firefox an accidental competitive edge (pcworld.com)

The change is about extension architecture, not a new Firefox feature. For users who depend on uBlock Origin, the browser has become a practical refuge from restrictions rolling through Chrome-derived products.

HN commenters also pointed to Brave and custom extensions, but the broader complaint was simpler: modern advertising has made blocking it feel necessary for ordinary browsing.

657,607 old links expose the web’s disappearing memory (0.mk)

The project followed 657,607 historical links after recovering a 0.mk backup. The count turns link rot from an anecdote into a record of a web that quietly vanished.

HN’s reaction was not nostalgia alone: readers pointed out that archives are a design problem, not a promise the original web ever made.

🔥Hot Discussion ★ 133 · 💬 116 · Aug 14 · #culture#data#web#0.mk#Hacker News

Gentoo closed Bugzilla after AI scraping overload (social.treehouse.systems)

Gentoo’s Bugzilla closure is a concrete maintenance incident: an issue tracker became unavailable because automated scrapers imposed more load than the volunteer-run service could sustain.

The HN thread asked whether rate limits, mirrors, terms, and bot identification can protect public infrastructure without making it less useful to humans.

🚀Tech ★ 152 · 💬 105 · Aug 9 · #AI#open source#web#Bugzilla#Gentoo

Another GitHub outage turns CI dependence into operational risk (githubstatus.com)

GitHub reported degraded availability for Actions and Pages, interrupting two services many teams use to build, deploy, and publish.

Developers in the thread were less interested in the status page than in the accumulated reliability cost of treating hosted CI as invisible infrastructure.

Accessibility needs ramps before it needs another expensive device (sightlessscribbles.com)

The essay’s central contrast is concrete: a costly stair-climbing wheelchair is easier to pitch than better doorknobs, ramps, and accessible buildings. Readers expanded that criticism to semantic HTML and other basics whose value is broad but whose funding story is less glamorous.

The strongest dissent matters too: new assistive technology can expand where someone can go, even if it does not excuse inaccessible infrastructure. The practical failure is treating one as a substitute for the other.

Readers now treat synthetic blog art as a warning label (nelson.cloud)

The complaint is not simply that generated images look strange. They can signal that a post was assembled quickly, with the same incentives that produce generic prose and unverified claims.

That makes the image an editorial choice, not a decorative one: it can either establish authorship or ask the reader to lower their guard.

🔥Hot Discussion ★ 739 · 💬 436 · Aug 5 · #AI#culture#web#AI

A color-space tool makes diverse skin tones a design parameter (toneyalexander.github.io)

The project turns a vague request for more inclusive visuals into a technical input developers can use when generating avatars, illustrations and examples.

HN's interest reflects a practical appetite for tools that make a design choice repeatable instead of requiring every team to rediscover it.

GitHub Trending: Last week — Seerr, GitHub CLI, systematic trading, Vue, KernelSU (github.com)

In GitHub Trending this week: Seerr manages media requests, GitHub CLI brings GitHub to the terminal, awesome-systematic-trading maps quant resources, Vue powers web interfaces, and KernelSU provides kernel-based Android root. The common thread is control over tools people already run.

Google News users say date filters no longer mean recent news (elgan.com)

Mike Elgan says Google News now returns social-media pages and results from the wrong country or language, while searches limited to the past week can surface stories that are weeks or months old.

Readers did not merely complain: they named paid alternatives such as Kagi and Ground News, suggesting that basic control over ranking has become a product feature.

🌍Other ★ 255 · 💬 181 · Aug 2 · #big tech#web#Google#Google News#Ground News+1

Chrome fixed 1,072 security bugs in two releases with AI (blog.google)

The jump is not a single bug-finding demo: Chrome 149 and 150 shipped 1,072 fixes after the team connected model-assisted discovery to triage, patching, testing, and release work.

The uncomfortable constraint is delivery. A public fix can become an attacker’s roadmap before it reaches users, so Google is also piloting two security releases a week and exploring dynamic patching.

🚀Tech ★ 483 · 💬 490 · Aug 1 · #AI#big tech#security#web#Chrome#Gemini#Google+1

Google lost a scraping case, and HN noticed the historical irony (techdirt.com)

The ruling concerned Google’s attempt to stop scraping through a DMCA theory. Readers saw a narrower legal loss and a broader market signal about access to results after affordable official APIs have become scarce.

The thread’s strongest refrain was not that scraping is consequence-free. It was that restricting the interface while leaving demand intact invites exactly the intermediaries Google is suing.

📈Biz ★ 264 · 💬 103 · Jul 28 · #big tech#policy#web#DMCA#Google#SerpApi

Removing React meant relearning where an interface should live (misago-project.org)

The migration moved interactivity toward server-rendered HTML with htmx rather than a large client application. That trade changes the boundary of the system more than it changes a library name.

The useful question from the thread is not whether React is bad. It is whether the product really needs a client-side state architecture before it needs simpler operations.

🚀Tech ★ 231 · 💬 158 · Jul 28 · #dev tools#programming#web#htmx#Misago#React

Europe can remove cookie banners with one browser setting (killthecookiebanner.eu)

The campaign says tracking is already prohibited by default, yet deliberately misleading consent dialogs push as many as 90% of visitors to accept while only about 3% want tracking. Its proposed fix is an automated browser signal.

HN’s catch is historical: Do Not Track also let browsers state a preference, and websites could ignore it. The hard problem is not sending the signal; it is making the recipient honor it.

A Namecheap account-takeover story turns into a registrar escape plan (news.ycombinator.com)

Several HN readers described abrupt account locks, weak support, or similar takeovers at other registrars. The recurring advice was operational rather than ideological: use domain privacy, keep recovery information current, and make a migration plan before an emergency.

The thread also undercuts the easy explanation that one company is uniquely broken—social engineering remains a human process wherever a support channel can reset access.

Brolly’s compact weather page wins HN, then gets asked to become a real text service (brolly.sh)

The site’s appeal is not a new forecast model; it is information design. Readers praised the compact layout and historical-temperature context, while pointing out that a minimal web interface is not automatically a text interface for scripts and terminals.

The requests were concrete: render plain text for curl, make narrow layouts work, reduce refresh delay, and give precipitation the same compact visual language as the rest of the forecast.

🌍Other ★ 133 · 💬 43 · Jul 26 · #dev tools#web#Brolly#Open-Meteo#wttr.in

Reddit called old.reddit.com a safety risk. A developer's browser logs told a different story (cole-k.com)

Reddit now requires login to view old.reddit.com, framing it as a safety measure against scraping. A developer's own request logs show the new interface is heavier, slower to build, and phones home constantly.

The real motive surfaced fast: Reddit has licensing deals with OpenAI and Google, and blocking the lightweight old interface makes it harder for rival AI companies to scrape training data for free.

The article's own author showed up in the thread: nuke old Reddit outright if you mean it, he wrote — don't hide an economic decision behind a security excuse.

🚀Tech ★ 371 · 💬 377 · Jul 23 · #privacy#social media#web#Google#OpenAI#Reddit

He tried Google, DuckDuckGo, Brave, and a self-hosted SearxNG. He went back to a paid search engine (blog.melashri.net)

After trying Google, DuckDuckGo, Brave Search, Qwant, and a self-hosted SearxNG instance, a blogger resubscribed to Kagi — a paid search engine — and wrote up exactly why nothing else stuck.

Google was the biggest letdown: "terrible" results, prioritizing multimedia over the plain text he was actually searching for — "I just want to look up some text."

The clincher wasn't search quality alone — it was Kagi's built-in custom CSS support, letting him restyle the interface in a way he couldn't reproduce with userscripts on any competitor.

🌍Other ★ 235 · 💬 184 · Jul 23 · #privacy#web#DuckDuckGo#Google#Kagi

Firefox 153 previews 'new' Containers a user traced back to 2017 (blog.mozilla.org)

Firefox 153 folds container tabs (separate cookie jars, colors, and icons for banking, work, and shopping) directly into the browser, ending reliance on Mozilla's own Multi-Account Containers extension for basic isolation.

The pushback was immediate: a reader traced the same interface back to a 2017 Mozilla documentation snapshot and a 2023 support page, arguing the 'preview' label hides that containers have quietly existed for years.

A hobbyist's air-traffic-control browser game had its leaderboard hacked within hours (airport.apunen.com)

You drag each color-coded plane's path by hand to the runway threshold that matches it, landing and launching before two aircraft collide. There's no tutorial: players spent their first minutes inventing their own routing rules, then their next minutes crashing anyway.

A Principal Engineer at AWS who works on EKS showed up with a detailed list of interface fixes. Someone else had already worked out you could just POST a fake score straight to the API, and the board filled with ten-thousand-landing runs that never happened.

A 'native HTML' UI kit turns out to run 40 JavaScript widgets nonstop (jelly-ui.com)

The library ships as 40 zero-dependency web components — jelly-button, jelly-otp, jelly-range, jelly-dialog — dropped onto a page with one script tag. Dark mode, right-to-left layout and WCAG AA color tokens come built in.

A reviewer found the six-box OTP input repeats a known anti-pattern, plus undersized hit targets on pagination. One reader flipped the critique: the same squishy hit-boxes could make tiny buttons far easier to hit for anyone without fine motor control.

98% browser support sounds safe. The thread did the math and it isn't (whynothugo.nl)

His thesis lands as a rule: 'truly robust engineering isn't about what works for most; it's about gracefully handling the edge cases.' The thread split on whether that framing is even right.

The sharpest replies went past the post itself: 98% quietly compounds. At 99% right per step a 20-pane dashboard breaks nearly one load in five, and an LLM that nails 99% of tool calls still fumbles almost every session.

🚀Tech ★ 473 · 💬 313 · Jul 8 · #AI#programming#web#CSS nesting#CUDA#Sass

A study says US vendors serve Europe's websites. A rival study found the opposite (ciphercue.com)

The catch: the scan only sees who answers the DNS query, the front CDN, not where the data actually lives. Cloudflare 'wins' every market precisely because it's the proxy, not the host.

So one reader re-ran the question against 50,000 API subdomains with the CDN fronts stripped out and got the reverse answer: Europe leans on OVH and Hetzner more than AWS. Another, claiming access to better data, said the numbers are off by roughly half.

The gym-shorts drawstring trick HN keeps resharing turns out to be the Lapp knot (youtube.com)

Knot-tiers pinned it fast: a slipped sheet bend, a join sailors have used for generations. The thread's sharper turn was that the clever knot may be beside the point, since most loose ties, one commenter argued, are just a granny knot tied where a square knot belongs, no new technique required.

And the very loop that makes this one adjustable is, a programming-language maintainer warned, exactly what makes it less secure; several people said skip knots entirely and use a cord lock.

Astro 7's Rust compiler promises 15–61% faster builds. One developer's got slower. (astro.build)

The rewrite runs deep. The rendering engine is about 2.4x faster, and Astro moves to Vite 8 with the new Rolldown bundler, which the team clocks at 10-30x faster than Rollup. Several sites now build more than twice as fast as on v6.

But the thread caught the asterisks. Strict HTML compilation now errors on unclosed tags, which blocks upgrading any site that pulls in messy remote content. One developer reported builds that got slightly slower, not faster. And the engineer who wrote the new Rust compiler is in the thread, taking questions.

🚀Tech ★ 183 · 💬 52 · Jul 8 · #dev tools#programming#web#Astro#Hono#Rust+1

A developer audited the YC CEO's 37K-lines-a-day AI site. Then HN audited the audit. (fastcompany.com)

The frontend weighs 6.42 MB across 169 requests; Hacker News, also run by YC, serves its homepage in seven requests and 12 KB. The auditor, Gregorein, confirmed the whole list by feeding the files to a single Claude session.

That is where the thread turned on the auditor: anyone with a Claude subscription could run the same check, several noted, and Fast Company's own page pulls 29 MB over 300+ requests. The critique that outlived the pile-on wasn't about the bloat at all. It was about measuring work in lines of code.

A community forked Organic Maps over a hidden Kayak deal, and shipped CoMaps (comaps.app)

The pitch: offline search and routing that need only a GPS fix, zero mobile data, and an app that says it collects no information about you at all.

The catch users keep hitting is search, with no way to blend city with name, road with category, or filter by opening hours.

Cloudflare put a cache in front of Workers — and quietly started billing free requests (blog.cloudflare.com)

The surprise is in the invoice: requests that used to be free, like static assets and worker-to-worker calls over service bindings, now bill at the standard request rate because each one first checks the cache.

One developer's flat verdict on the new charges: 'that sounds like a bug that just happens to generate them more money.'

Amazon blocks new downloads on old Kindles, so a 50-books-a-year buyer starts torrenting (reprog.wordpress.com)

The on-screen message draws the line: previously downloaded books still open, but the device can no longer pull new purchases from the Kindle store. So he built a workaround, buy on Amazon, torrent a DRM-free copy, sideload over USB, and admits the purchase step now delivers no benefit whatsoever.

Not everyone sees malice. One reader whose own older Kindle still sideloads says the block only hits the store on end-of-life devices, whose ancient built-in browser was never going to last.

A live map of Britain's trains, some ploughing through the M25 and Channel (map.signalbox.io)

The clever part is how Signalbox says it works: it identifies which train a phone is riding by matching a snapshot of the device's data to each train's trajectory, with no background location tracking and no hardware. Slick in theory.

In practice, locals weren't impressed. One watched a Liverpool Street service plough across the M25, forty miles off its route; another who lives beside a line calls the whole thing as good as useless.

Organic Maps hit 6 million installs — and the thread points newcomers to its fork instead (organicmaps.app)

The pitch is clean: 100% of features work offline, no ads, no registration, verified tracker-free, 6 million installs by December. Then a CoMaps contributor shows up in the thread recruiting iOS developers, and others start listing why the community walked out a year ago — quietly added ads, a slice of code turned proprietary, donations that allegedly went missing.

The awkward footnote from a long-time user: even fans admit the search is so bad they keep crawling back to Google Maps.

"Web crypto is always snake oil" — and the cryptographers show up to disagree with each other (devever.net)

Landau calls it an "incoherent cryptosystem": the server that wants to read your messages is the same server shipping the JavaScript that's supposed to stop it — and it can push different code to one IP at any moment. He extends the charge to Signal, WhatsApp and iMessage.

The pushback is credentialed on both sides. One security researcher says you can build Signal from source yourself, so it doesn't apply — then, in the same breath, points out iMessage isn't really end-to-end anyway because iCloud Backup is on by default.

shadcn didn't ship a codemod for the Radix-to-Base-UI switch — it shipped an LLM "skill" instead (ui.shadcn.com)

shadcn/ui now defaults to Base UI over Radix (Base UI at v1.6.0, 6M+ weekly downloads; users picked it 2-to-1). Radix isn't deprecated. The migration story is the twist: an LLM-driven skill, component by component, instead of a deterministic codemod.

The thread's unease is about tone and trust: if even a flagship release note is visibly AI-written, where's the line — and does replacing codemods with an agent trade repeatability for vibes?

🚀Tech ★ 275 · 💬 154 · Jul 6 · #AI#dev tools#web#Base UI#Radix#React+1

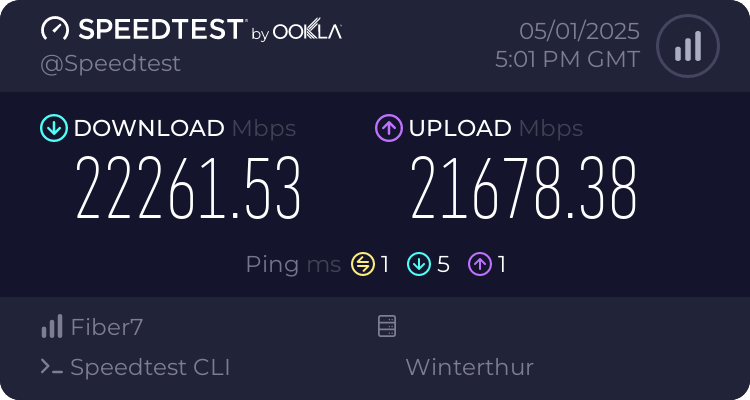
Switzerland's 25 Gbit fiber isn't the free market winning — it's a regulator forcing four fibers to every home (stefan.schueller.net)

The post's argument: cheap symmetric 25 Gbit isn't a free-market miracle but the result of treating last-mile fiber as a regulated natural monopoly — four strands per home, point-to-point, any ISP gets equal physical access, and you switch providers with a phone call.

The thread doesn't let the framing stand. Speedtest's index shows Swiss average speeds roughly matching the US; the States already sells 25–50 Gbit in places; and the real variable, one commenter argues, isn't speed or density but who controls the last mile.

🌍Other ★ 527 · 💬 418 · Jul 4 · #economy#policy#web#Init7#Swisscom#UTOPIA+1

SearXNG's own creator shows up to say the whole metasearch idea is a dead end (github.com)

SearXNG aggregates results from many search services without tracking or profiling users, is self-hostable, AGPL-licensed, and increasingly used as a search backend for local LLMs and agents — 33.2k stars, 280+ contributors.

Then the person who started it all posts: he left the metasearch concept behind over its limitations and now builds a full-text indexer instead. And the privacy premise gets its own puncture — you've swapped one watcher for hundreds.

A reader asked a blogger to sound less British. His one-word answer started 400 comments (shkspr.mobi)

The refusal wasn't the story; the argument under it was. Eden's point: a language tag isn't a wall, it's a signature — the culture he lives in, the way he thinks, the accent he writes in — and encountering something unfamiliar is a feature, not a bug.

Then the thread did the thing the post was about. A developer had actually built the Accept-Language easter egg the piece only gestured at, serving Brits a different site entirely. And when a commenter fretted for Eden's 'safety,' the author himself dropped in to reply, in full character: 'OP here. Fuck off.'

PeerTube can serve a video to thousands without a big server. The thread explained why that still isn't YouTube (github.com)

It's a free, federated video platform from the French nonprofit Framasoft: no ads, ActivityPub federation with the Fediverse, and peer-to-peer playout so simultaneous viewers offload bandwidth from the host.

A working YouTuber did the money math and it was brutal — a ~100K-subscriber channel that couldn't survive on under $500–$1,000 a video, which PeerTube has no way to provide. As one authority put it: the tech does exactly one of the four jobs a YouTube replacement needs, and it does that one fine.