An Edge exploit chain with no memory corruption starts by visiting microsoft.com
Orange Tsai's Pwn2Own entry needed no heap tricks. Five logic bugs and two Windows features were enough to run a planted binary.
Edge auto-creates and signs into a Microsoft account profile when you visit a Microsoft site, and a CORS misconfiguration on assets.msn.com lets any website read the signed-in email. From there the chain abuses a navigation throttle, a popup whitelist and a diagnostic-log file write to launch a planted telnet.exe.
It earned $175,000 at Pwn2Own Berlin 2026, and its author says no AI was used to build it.
Five bugs and two Windows features, no memory corruption
Orange Tsai's writeup starts with Edge's Conditional Access navigation throttle, which starts navigations from the browser process and defaults to the active tab, producing a universal XSS on sites like google.com. An origin check using GetLastCommittedURL() misses navigations from other windows, and a hardcoded popup whitelist lets about:blank#quickAuthPopup through.
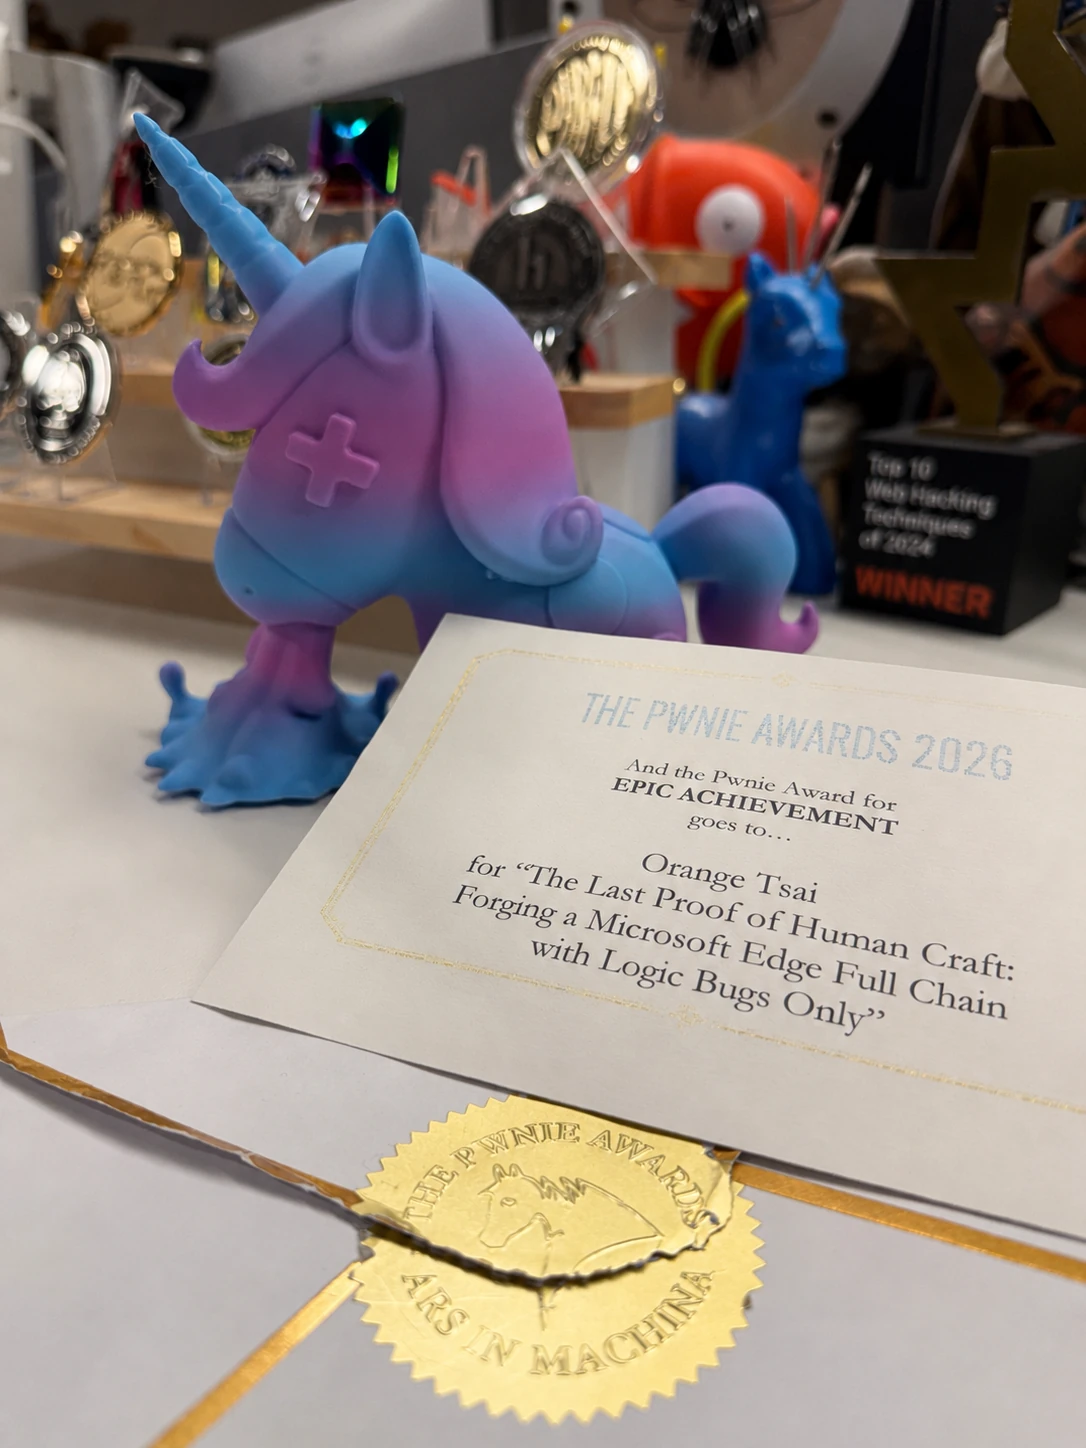
Sign-in is the quiet enabler: a visit to a Microsoft site makes Edge create and sign into a profile, and the CORS flaw on assets.msn.com leaks the email. The escape runs through the Immersive Reader read:// scheme (missing from Chromium's privileged-page blocklist) and zipDiagnosticLogFiles(), whose path traversal and null byte overwrite protocols.json. A restart then lets Windows resolve a missing telnet.exe from a user-writable WindowsApps folder. The exploit is under 100 lines, built over about two months, and it won Pwn2Own Berlin 2026 ($175,000, 17.5 Master of Pwn points) and a Pwnie for Epic Achievement.
Readers were more bothered by the profile than the exploit
The writeup's line that merely visiting microsoft.com makes Edge create a profile and sign you in drew the sharpest reaction:
"This is disgusting behaviour, RCE chain or not." — a commenter reacting to the auto sign-in
Another pointed to a companion talk that pops Edge from the calculator app (
, shared by a commenter who praised the chain).For defenders, the reading is that none of the five bugs would be caught by memory-safety mitigations. They are product-integration decisions: a browser that trusts Microsoft-owned origins enough to skip popup and origin checks.
Get breakdowns like this every day
The top Hacker News stories, unpacked — by email, Telegram, or RSS.
Redraw the world by IPv4 addresses and a thread argues about India's 47 million
IP Trust rescaled every country's land area to its share of 3.6 billion locatable addresses. The comments went straight to who lives behind a shared IP.