Tag

iMessage

2 stories

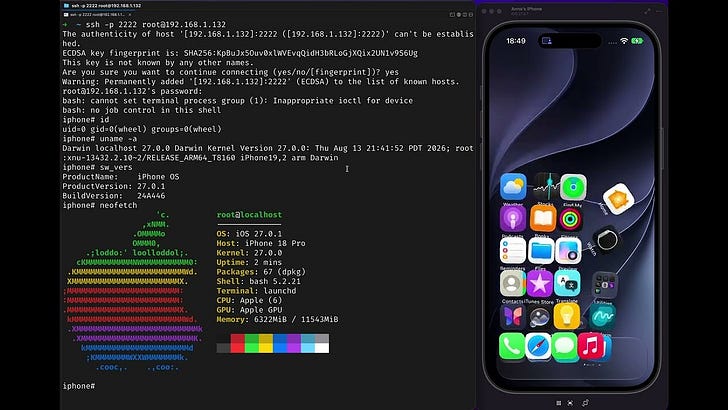
Security firm roots an iPhone from a PDF in iMessage, then posts only demo videos (blog.calif.io)

The demos show a malicious PDF opened through iMessage or Signal ending in code execution, followed by an app that roots the phone. Calif says most of the bugs behind them already went to Apple.

The thread split over a different question: is it responsible to show a working takeover before a patch exists, or is the publicity what gets people to update?
Not just a headline — the discussion unpacked

The top HN threads: facts from the discussions, both sides, insider voices. Email, Telegram, or RSS.

"Web crypto is always snake oil" — and the cryptographers show up to disagree with each other (devever.net)

Landau calls it an "incoherent cryptosystem": the server that wants to read your messages is the same server shipping the JavaScript that's supposed to stop it — and it can push different code to one IP at any moment. He extends the charge to Signal, WhatsApp and iMessage.

The pushback is credentialed on both sides. One security researcher says you can build Signal from source yourself, so it doesn't apply — then, in the same breath, points out iMessage isn't really end-to-end anyway because iCloud Backup is on by default.