Tag

Calif

3 stories

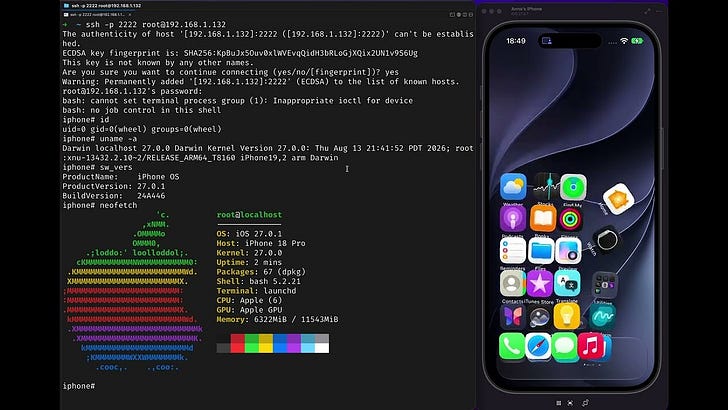
Security firm roots an iPhone from a PDF in iMessage, then posts only demo videos (blog.calif.io)

The demos show a malicious PDF opened through iMessage or Signal ending in code execution, followed by an app that roots the phone. Calif says most of the bugs behind them already went to Apple.

The thread split over a different question: is it responsible to show a working takeover before a patch exists, or is the publicity what gets people to update?
Not just a headline — the discussion unpacked

The top HN threads: facts from the discussions, both sides, insider voices. Email, Telegram, or RSS.

PHP patched two unauthenticated RCE bugs after the CVE IDs leaked two days early (thephp.foundation)

PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 shipped on 21 October, a day ahead of plan, after the CVE IDs leaked. Both bugs score CVSS 9.2 and need no login, and a proof-of-concept video went up by mistake.

In the thread, an admin racing across several servers said a three-line nginx rule blocking multipart uploads had been quietly protecting a machine he could not shut down.

🚀Tech ★ 683 · 💬 336 · 7 days ago · #open source#security#web#Calif#Chainguard#PHP+1
