Tag

LinkedIn

2 stories

He inspected his take-home coding test with tree -a. It had a hidden .git folder full of malware (citizendot.github.io)

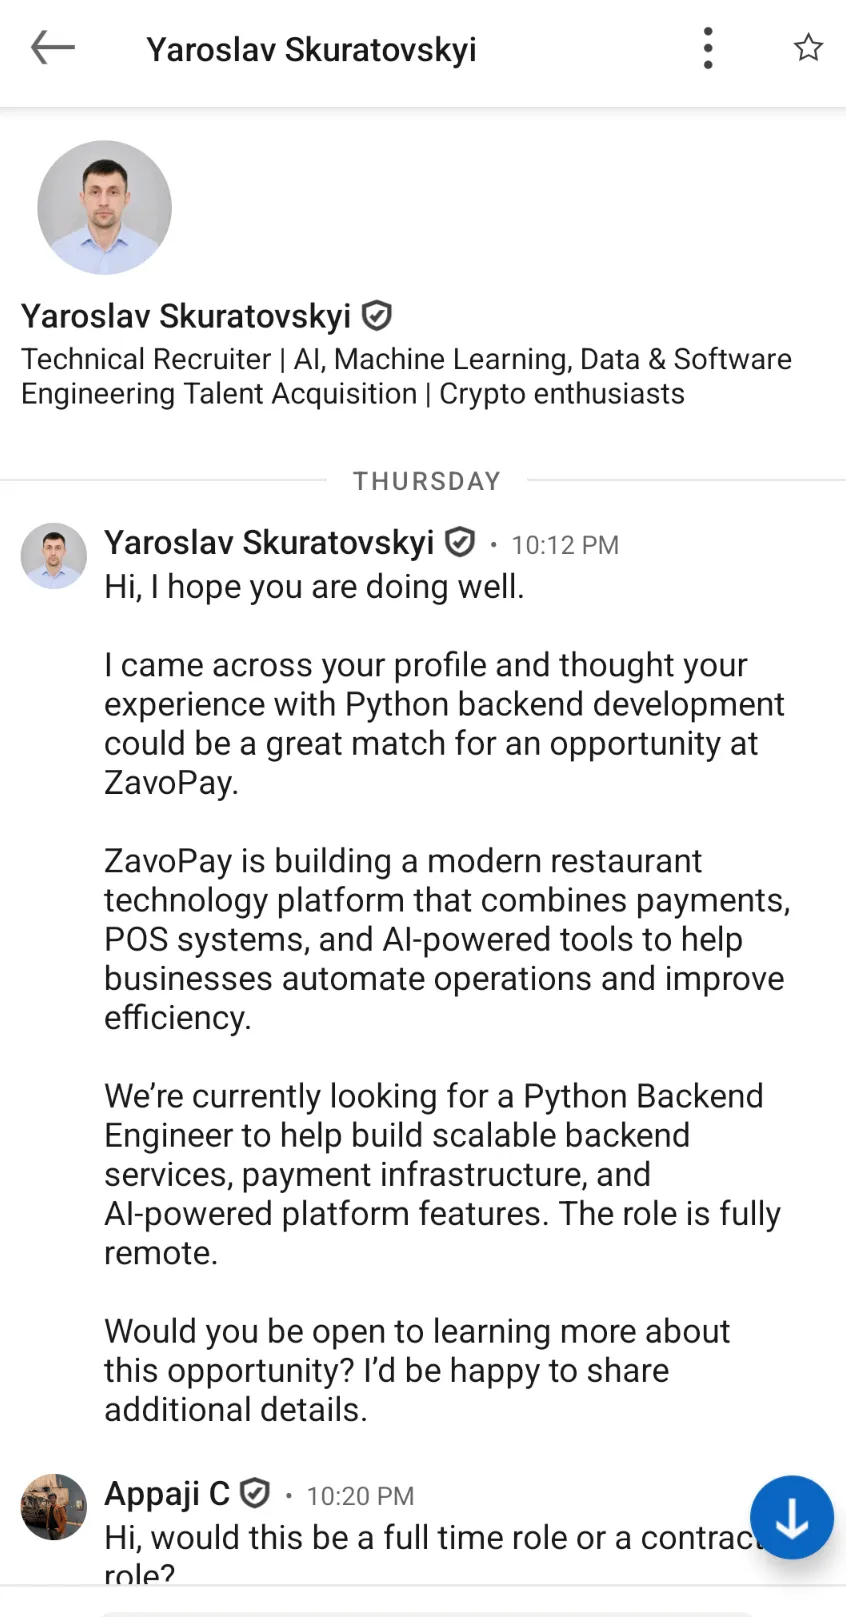
A fake Y Combinator recruiter sent a Python take-home test with a hidden pre-commit Git hook wired to a remote server — the moment you'd run `git commit`, it would fingerprint your OS and silently download stage two.

The attacker cloned a real, innocent FastAPI project off GitHub and just swapped in a malicious `.git` folder, then customized a unique payload ID per victim.

The final-stage script pulled in `hardhat`, an Ethereum dev toolkit — this wasn't credential theft, it was built to reach into crypto wallets.
🚀Tech ★ 342 · 💬 88 · Jul 23 · #security#FastAPI#GitHub#LinkedIn

Not just a headline — the discussion unpacked

The top HN threads: facts from the discussions, both sides, insider voices. Email, Telegram, or RSS.

A recruiter sent a GitHub repo to 'review.' The npm install was the attack (roman.pt)

Running npm install would have been enough. The package's prepare script auto-runs a file that, buried under walls of commented-out tests, fetches and executes whatever a remote server sends back.

He never cloned it locally. He spun up a throwaway VPS, pointed a read-only AI agent at the tree, and it flagged app/test/index.js almost immediately. The thread's verdict on who's behind it was fast and grim: DPRK.