Security firm roots an iPhone from a PDF in iMessage, then posts only demo videos (blog.calif.io)
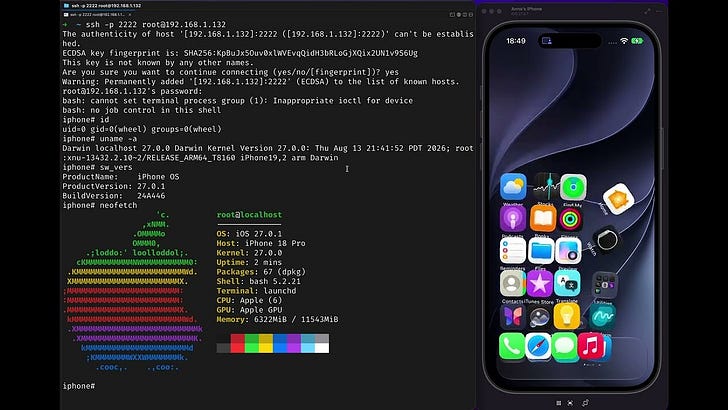
The demos show a malicious PDF opened through iMessage or Signal ending in code execution, followed by an app that roots the phone. Calif says most of the bugs behind them already went to Apple.
The thread split over a different question: is it responsible to show a working takeover before a patch exists, or is the publicity what gets people to update?
Sign in to save