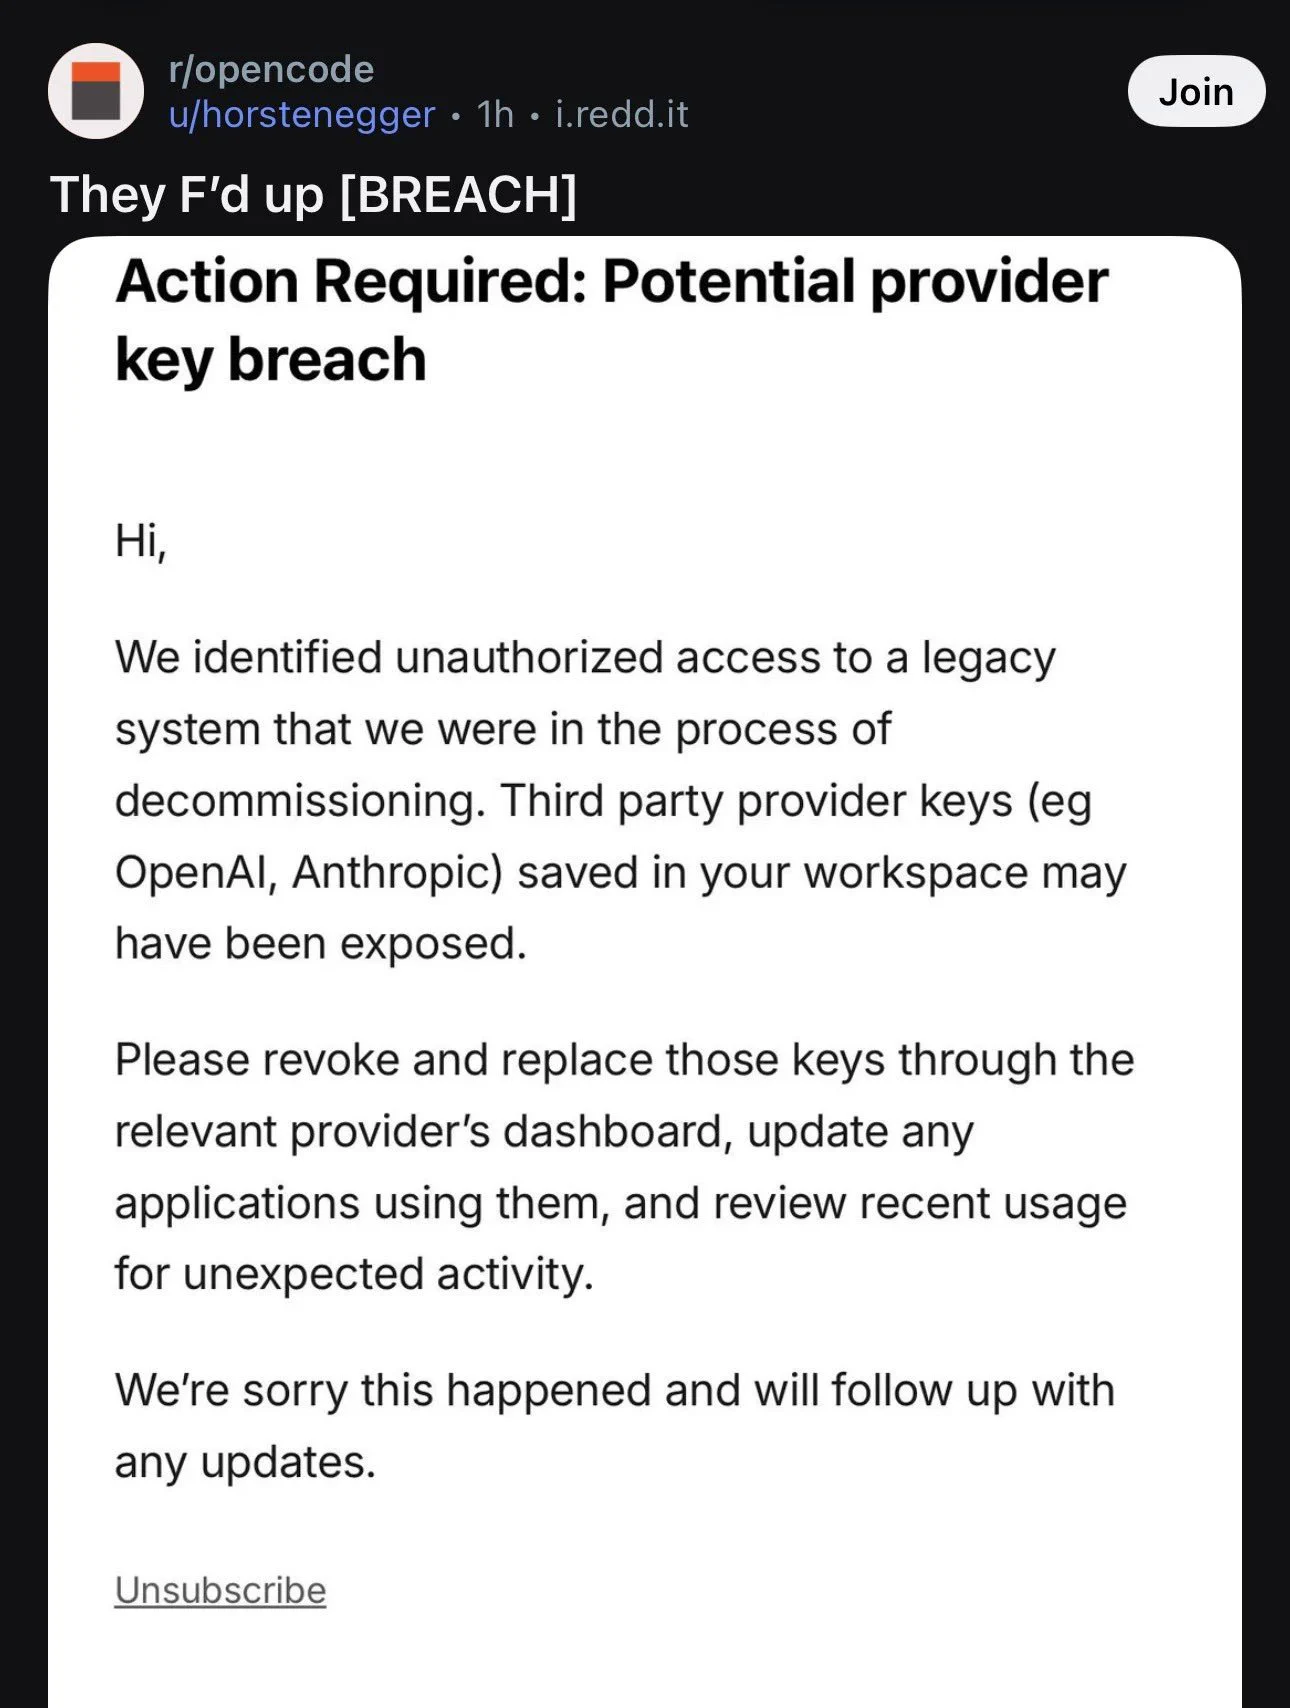
OpenCode's leak hit stored API keys, not the coding agent most users run (twitter.com)
The breach is in 'OpenCode Console', an OpenRouter-like service where users paste provider API keys so it can proxy their requests. People running only the open-source terminal agent or desktop app are not affected.
Several commenters noted the Console had no visible privacy policy or terms of service and that the team's announcement never drew that line.
Sign in to save